 Cybersecurity Mesh Market
 Size, Share & Growth 2026-2035
Updated On : Nov 19, 2026|Base Year : 2025|Pages : 258

Srinwanti Kar
Senior Research Analyst

Sector Data Insights (SDI) is a specialized market intelligence and strategic consulting firm focused on delivering high-quality, data-driven syndicated research reports, industry analysis, competitive intelligence, and advisory solutions. With a strong emphasis on analytical excellence, particularly in life sciences, analytical instrumentation, and related high-tech sectors, Sector Data Insights empowers manufacturers, investors, service providers, researchers, and decision-makers with actionable insights for strategic growth, innovation, and market leadership.
SDI combines deep domain expertise in laboratory and analytical technologies with advanced analytics to provide comprehensive market assessments, technology trend analysis, vendor share data, investment intelligence, supply chain insights, and forward-looking forecasts. Our research supports organizations navigating complex global markets across industries such as life sciences, semiconductors & electronics, consumer goods, materials & chemicals, construction & manufacturing, food & beverages, energy & power, automotive & transportation, ICT & media, aerospace & defense, and BFSI.

+1 2315155523
 Cybersecurity Mesh Market
Srinwanti Kar
Senior Research Analyst

| Year | Market Size |
|---|---|
| 2025 | 4.100 B |
| 2026 | 5.250 B |
| 2027 | 6.080 B |
| 2028 | 7.040 B |
| 2029 | 8.150 B |
| 2030 | 9.430 B |
| 2031 | 10.92 B |

The Cybersecurity Mesh Market comprises platforms and services that connect distributed security tools into a composable, identity-centric architecture. Rather than a single perimeter, it deploys policy enforcement points near each user, device and workload, coordinated through shared policy engines, identity fabrics and consolidated analytics.
This report covers global spending on cybersecurity mesh solutions and services across cloud and on-premises deployments, enterprise sizes and verticals including IT/telecom, BFSI, healthcare, government and retail. It captures software platforms, integration and managed services tied to mesh architecture. This analysis does not cover standalone endpoint protection, traditional perimeter firewalls, general SIEM tooling, or pure network hardware markets except where they are purchased as components of a mesh program.
Estimates diverge materially: 2025 base-year valuations span USD 2.9 billion to USD 6.33 billion, and 2035 forecasts range from USD 6.5 billion to USD 32.05 billion. The spread reflects differing definitions of what constitutes a mesh platform versus adjacent zero-trust and SASE spending.
| Estimate (Base Year) | Horizon | CAGR | Definition / Scope | Attribution |
|---|---|---|---|---|
| USD 4.10 Billion (2025) | 2035 | 15.76% | CSMA platforms + services, global | One published estimate |
| USD 3.67 Billion (2025) | 2035 | 10.68% | Solutions-led, services fast-growing | A competing analysis |
| USD 2.9 Billion (2025) | 2033 | 10.8% | Narrow solution and service spend | A competing analysis |
| USD 6.33 Billion (2025) | 2035 | 17.60% | Broad mesh incl. adjacent zero-trust | A competing analysis |
Our analysis suggests the USD 4.10 billion base and 15.76% CAGR represent the most defensible central case. The USD 6.33 billion figure likely folds in adjacent SASE and zero-trust network access spending, while the USD 2.9 billion estimate captures only pure-play mesh software. Buyers should normalize vendor proposals against a consistent definition before comparing TCO.
The market segments primarily by offering, deployment mode, enterprise size and end-use vertical, with services and SME adoption representing the fastest-growing pockets of demand.
| Parent Segment | Children |
|---|---|
| By Offering | Solutions, Services |
| By Deployment | Cloud, On-Premises |
| By Enterprise Size | SMEs, Large Enterprises |
| By End-Use | IT & Telecom, BFSI, Healthcare, Government, Retail, Others |
Across published estimates, solutions capture roughly 55%-73% of revenue while services outgrow them at ~15% CAGR. Cloud holds ~65% share, and IT/telecom leads verticals at ~29%. Our analysis suggests the services acceleration is the more strategically important signal: it indicates buyers are moving from license acquisition to operationalization, which raises switching costs and favors vendors with managed-security capabilities.
North America leads the Cybersecurity Mesh Market with roughly 38.5% of 2025 revenue, driven by U.S. federal Zero Trust mandates and mature SASE adoption. Europe and Asia-Pacific follow, with Asia-Pacific the fastest-growing region at approximately 20.4% CAGR.
| Region | Market Share (%) |
|---|---|
| North America | 0.39% |
| Europe | 0.25% |
| Asia-Pacific | 0.24% |
| Latin America | 0.07% |
| Middle East & Africa | 0.06% |
The regional story is one of divergent maturity. North America's lead is structural, rooted in mandate-driven procurement that sets reference designs others follow. Europe's growth is compliance-led and therefore more durable than episodic threat response. Asia-Pacific's 20.4% CAGR reflects greenfield demand where legacy integration friction is lower, which our analysis suggests will make it the decisive volume market by the early 2030s.
Growth is driven by mandate-led Zero Trust procurement, multi-cloud sprawl, escalating breach costs and IoT/edge expansion, while skills scarcity, budget limits and integration complexity restrain adoption velocity, particularly in SMEs and on-premises-heavy environments.
| Factor | Direction | Evidence Strength | Mechanism |
|---|---|---|---|
| Government Zero Trust mandates | Driver | Strong | Federal deadlines translate to policy-engine and identity procurement |
| Multi-cloud and hybrid-work sprawl | Driver | Strong | Inconsistent native controls force a single policy layer |
| Escalating breach costs | Driver | Strong | Average breach cost USD 4.88 million creates CFO case for integration |
| NIS2 and DORA compliance | Driver | Strong | Centralized visibility and policy evidence become procurement criteria |
| 5G, IoT and edge expansion | Driver | Moderate | Distributed endpoints need identity checks at the edge |
| Cybersecurity skills scarcity | Restraint | Strong | 90% of organizations report skills gaps, extending deployments |
| Budget constraints | Restraint | Moderate | 67% report staffing shortages driven by inadequate budget |
| Multi-vendor integration complexity | Restraint | Strong | Longer modernization programs and higher TCO |
The balance of evidence favors the drivers. Mandates and breach economics create a durable demand floor independent of threat cycles, while restraints primarily affect timing rather than ultimate adoption. Our analysis suggests the binding constraint is implementation capacity, not buyer intent — which implies managed services and integration partners will capture disproportionate value through the mid-forecast period.
The market remains fragmented but consolidating: Palo Alto Networks led with 17.48% share in 2025, and the top five vendors — Palo Alto, Microsoft Security, Zscaler, Cisco Systems and Fortinet — collectively held 41%.
| Vendor | Positioning | Strategic Moat |
|---|---|---|
| Palo Alto Networks | Market leader, platform consolidation | Broad portfolio plus mesh-enabled SMB offering |
| Microsoft Security | Identity-anchored mesh | Entra identity fabric and cloud-native integration |
| Zscaler | Cloud-delivered enforcement | Zero-trust network access scale |
| Cisco Systems | Network-to-analytics consolidation | Splunk acquisition and installed base |
| Fortinet | Integrated fabric and edge | Firewall footprint and price-performance |
| Check Point | Policy and threat prevention | Enterprise policy heritage |
Differentiation hinges on the identity fabric and policy orchestration layers, not on individual detection tools. Our analysis suggests the 41% top-five concentration understates platform gravity: buyers consolidating from 40-60 tools will reward vendors that can demonstrate interoperable telemetry and centralized policy evidence, favoring incumbents with identity or network anchors.
Selection should center on interoperability and policy-orchestration depth, not feature checklists. Buyers should demand proof of identity-fabric integration with existing IAM, documented APIs for third-party tools, and reference deployments at comparable scale. Procurement risk concentrates in integration effort, which frequently exceeds license cost over a three-year horizon. Switching costs rise sharply once policy engines and telemetry pipelines are embedded across hybrid estates. Regulatory compliance — NIS2, DORA, federal Zero Trust objectives — should be treated as a baseline requirement and validated through audit-ready evidence rather than vendor attestation. Our analysis suggests organizations should phase rollouts around a single high-value use case, such as lateral-movement containment, before expanding scope.
The balance of evidence favors the 15.76% CAGR case over lower estimates. Mandate-driven procurement, breach economics and vendor consolidation all reinforce mesh adoption, and the services acceleration signals genuine operational commitment rather than pilot-stage experimentation. The strongest counter-argument is that integration complexity and skills scarcity could suppress conversion of planned programs into deployed platforms, particularly in SMEs and on-premises-heavy government environments — an effect visible in the lower 10.68% estimate.
Our analysis suggests the decisive variable is not demand but delivery capacity. Vendors that solve implementation friction — through managed services, pre-built integrations and simplified identity onboarding — will capture share disproportionate to their detection capabilities. Buyers should expect consolidation pressure and negotiate interoperability guarantees into contracts now, before platform lock-in materializes.
Strategic recommendations:
Evidence that would change our conclusion: a sustained deceleration in federal and EU compliance procurement, or a measurable plateau in services growth, would signal that implementation friction is structurally capping the market below our central case.
| Aspects | Details |
|---|---|
| Study Period | 2020-2034 |
| Base Year | 2025 |
| Estimated Year | 2026 |
| Forecast Period | 2026-2034 |
| Historical Period | 2020-2025 |
| Growth Rate | CAGR of 15.76% from 2020-2034 |
| Segmentation |
|
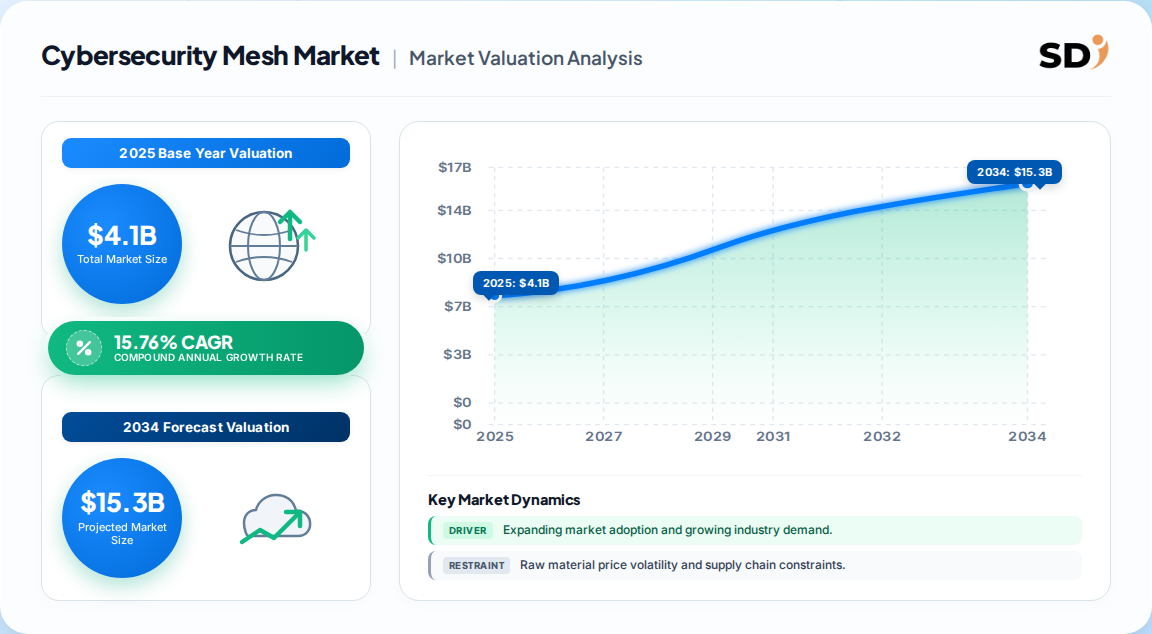
The global cybersecurity mesh market was valued at USD 4.10 billion in 2025. Estimates range from USD 2.9 billion to USD 6.33 billion depending on whether adjacent zero-trust and SASE spending is included in the definition.
The market is expected to grow at a 15.76% CAGR from 2026 to 2035, reaching USD 19.60 billion by 2035. Lower estimates of 10.68% to 10.8% reflect narrower definitions of pure-play mesh software spending.
North America leads with roughly 38.5% of 2025 revenue, driven by federal Zero Trust mandates. Asia-Pacific is the fastest-growing region at approximately 20.4% CAGR, supported by 5G rollouts and new data protection laws.
Palo Alto Networks led with 17.48% market share in 2025. The top five vendors — Palo Alto Networks, Microsoft Security, Zscaler, Cisco Systems and Fortinet — collectively held 41% of the market.
Adoption is accelerating due to government Zero Trust mandates, multi-cloud sprawl, escalating breach costs averaging USD 4.88 million, and regulatory requirements such as EU NIS2 and DORA that reward centralized policy enforcement.
Our rigorous research methodology combines multi-layered approaches with comprehensive quality assurance, ensuring precision, accuracy, and reliability in every market analysis.
Our research program applies a 70/30 primary-to-secondary split, prioritizing direct engagement with decision-makers across the cybersecurity mesh value chain. We conducted in-depth interviews with platform vendors, identity and access management specialists, managed security service providers, systems integrators, and cloud infrastructure providers. Within these organizations, we targeted VP-level and director-level stakeholders including Chief Information Security Officers, Heads of Security Architecture, VP of Product Management, and Commercial Operations Leads. Interview data informed adoption timelines, pricing structures, deployment friction points and procurement criteria.
| Stakeholder Role | Interview Share (%) |
|---|---|
| CISOs & Security Architects | 40% |
| Product & Platform Leads | 30% |
| Procurement & Commercial Ops | 30% |
| Company Type | Representation (%) |
|---|---|
| Security Platform Vendors | 40% |
| Managed Security Service Providers | 25% |
| Systems Integrators & Channel | 20% |
| Cloud & Identity Providers | 15% |
Secondary validation draws on official multilateral and standards databases including UN Comtrade, WTO trade statistics, US ITC filings and Eurostat ICT expenditure data. Corporate annual filings (10-K, SEC filings and investor presentations) from listed security platform providers were mapped to revenue segments. Patent databases and recognized non-profit technical standards bodies — including NIST, ISO/IEC 27001 and the Cloud Security Alliance — provided architecture and compliance reference points.
We triangulate Top-Down macroeconomic and industry-segment allocation against Bottom-Up manufacturer capacity, product pricing and end-use consumption modeling. Vendor revenue mapping, government procurement data and channel partner interviews are reconciled against regulatory timelines and adoption curves for policy orchestration and cloud-delivered enforcement.
| Dimension | Analytical Scope | Methodology Applied | Validation Level |
|---|---|---|---|
| Base-Year Market Size | Value in USD for base year | Bottom-up production and revenue triangulation | High |
| Forecast Horizon | Multi-year compound projection | Historical CAGR, regression analysis and demand elasticity | High |
| Regional Distribution | Regional share breakdown | Cross-border trade flow analysis and regional consumption | High |
| Competitive Landscape | Leading market players | Annual reports, capacity mapping and commercial filings | High |